News

DeepTech Forum Sophia Antipolis #2: A Look Back at a Day of Ecosystem Building, Embracing Failure, and Shaping the Future

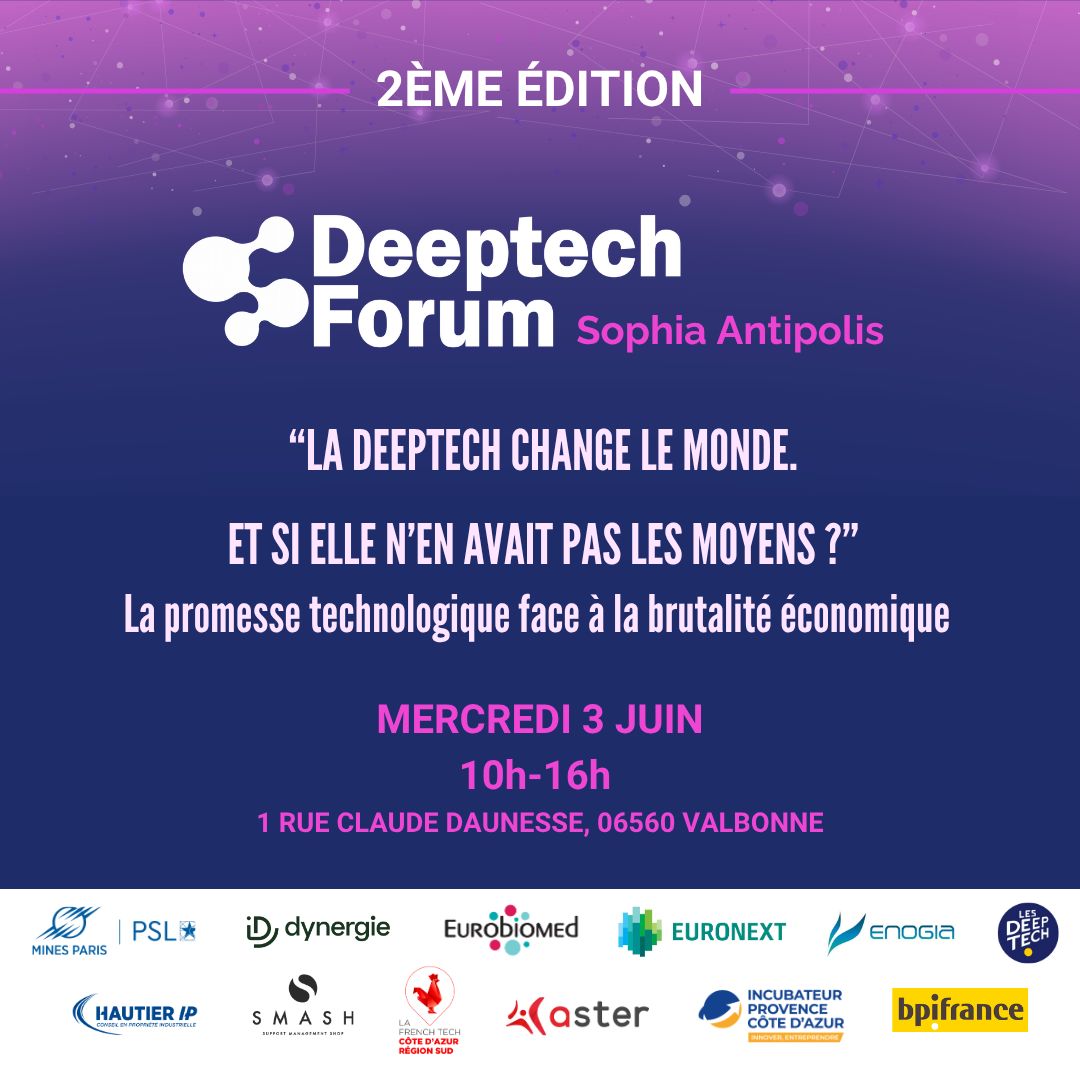
On June 3, we were invited to participate in the second edition of the DeepTech Forum Sophia Antipolis, organized by students in the Specialized Master’s in Deeptech Entrepreneurship and Innovation program at Mines Paris-PSL, in collaboration with Dynergie. It was a day dedicated to the ecosystem, open dialogue, and collective reflection on the future of disruptive innovation in the region. With a booth on the Pierre Laffitte Campus, we took advantage of the day to meet the Côte d’Azur deeptech community, share our approach to product cybersecurity, and talk with those who drive the ecosystem on a daily basis: entrepreneurs, researchers, investors, support organizations, students, and public sector representatives. At the booth, Nicolas conducted a series of demos of the MOABI platform, discussed our client use cases, and engaged in broader conversations about the role of a deep tech entrepreneur. A direct and rigorous approach to disruptive innovation The tone of the event, set from the outset by its patron Emilie Royère, director of Eurobiomed, did not seek to sugarcoat reality. This second edition chose to address disruptive innovation head-on, through candid and at times uncomfortable discussions. The most memorable panel discussion of the afternoon, titled “Failing in Deep Tech: Luxury, Choice, or Waste?”, clearly illustrated this approach. Failure in deep tech often remains a taboo subject, even though it is an integral part of the journey. Being able to discuss it publicly, with entrepreneurs who have weathered the storm and investors willing to speak candidly, is exactly the kind of conversation the ecosystem must be able to have if it is to mature. Later, the joint presentation by Euronext and Enogia traced the concrete path of a deep-tech company, from fundraising to its initial public offering. This is a rare journey in the French deep-tech innovation landscape and a valuable case study for the founders in attendance who are looking toward the long term. Sophia Antipolis 2035: Moving Beyond Denial The afternoon concluded with regional foresight workshops focused on the future of Sophia Antipolis and the French Riviera by 2035. We participated in the first workshop, whose topic left no room for complacency: Sophia has missed the deep tech curve. Why, and how can this be corrected? A direct, almost provocative statement that had the merit of sparking a frank discussion among students from Mines, active entrepreneurs, and local stakeholders in the technology park. Several key themes emerged from the discussions: the historical difficulty in transforming regional scientific excellence into industrial projects, the scarcity of the patient capital required for deep tech, competition from other better-structured French and European ecosystems, and the need to build stronger bridges between laboratories, specialized training programs, and established manufacturers. The exercise was not intended to produce an action plan. Its value lay elsewhere: collectively acknowledging the reality of the situation, without trying to sidestep it, is likely the prerequisite for any serious course correction. What we took away from the day Beyond the conferences and workshops, it was the quality of the informal exchanges that left a lasting impression on us. Whether at the booth, over coffee, or during the closing cocktail reception, we had lengthy conversations with founders who shared our concerns about growth, funding, recruitment, and the challenges of long-term tech entrepreneurship. A true convergence of perspectives on what it means to build a deeptech company in France today. We left the Pierre Laffitte campus having forged connections, identified follow-up projects, and with a strengthened conviction that this type of event, on a human scale and resolutely ecosystem-oriented, is essential to the maturation of regional deeptechs. A big thank you to the students of the Specialized Master’s in Deeptech Entrepreneurship and Innovation at Mines Paris-PSL, who designed and organized this event with a sense of community and a level of seriousness rarely seen at this stage of their education. Thanks also to Dynergie for its support, to Emilie Royère for sponsoring this edition, and to all the speakers and participants who made this day so enriching. See you next year, we look forward to it.
Read More »

Cyber On Board 2026: Screening 100 vulnerabilities a day under regulatory constraints, the challenge posed by Jonathan Brossard

The third edition of Cyber On Board concluded last night, following three days that confirmed a fundamental shift: embedded cybersecurity is no longer a technical niche reserved for a handful of specialists. It is becoming the focal point where regulatory compliance, technological sovereignty, and the operational resilience of critical industries converge. Jonathan Brossard, founder and CTO of MOABI, spoke on Wednesday, May 27, during the Software & Drones session on a topic that encapsulates this shift: Practical Vulnerability Triage Under Regulatory Pressure for Modern PSIRTs. Here are the key takeaways and the discussions it sparked with the industry representatives in attendance. An imbalance that has become structural The community now agrees on this basic fact: NIST published more than 40,000 CVEs in 2024, which amounts to over 100 new vulnerabilities to address every business day. Meanwhile, regulatory deadlines have tightened drastically: 24 hours for the Cyber Resilience Act and DORA, 72 hours for NIS2, 4 business days for the U.S. SEC Cyber Rule, and 15 days for CISA’s KEV catalog. The imbalance has become untenable. It is precisely this tension between volume and deadlines that now defines the daily reality for PSIRT teams and product security managers. The Pitfall of Publisher CVE Feeds The first limitation highlighted by Jonathan: purely governance-based approaches are no longer sufficient. Filtering CVEs by base CVSS score (≥ 9.0) and then rescoring them with environmental vectors seems reasonable. In reality, this method systematically eliminates kernel privilege escalation CVEs—all of which are local by definition—on systems not exposed to the Internet, even though they are part of the asset’s actual attack surface. The deeper issue remains data quality. The presentation was based on a benchmark conducted on Ubuntu 24.04 LTS, using Ubuntu Pro CVEs as a reference: Tool Detected CVE Precision Recall MOABI 1 329 100 % 100 % OpenSCAP 1 373 100 % 96,7 % Ubuntu Pro CVEs 2 084 63,7 % 99,9 % Of the 2,084 CVEs reported by the vendor reference source, 755 are false positives, representing a 36.3% error rate. In practical terms, a PSIRT team that relies solely on vendor feeds spends more than a third of its triage time on vulnerabilities that do not affect the targeted system. The technical reason is clear: matching by package name cannot determine whether the vulnerable symbol is actually present in the deployed binary, nor whether the distribution has backported a fix without changing the version number. Only verification at the binary level can resolve this. The Fuzzing Wall Second limitation: fuzzing, sometimes presented as the technical solution to the problem, does not scale. For CVE-2023-2804, a heap overflow in libjpeg-turbo, AFL++ finds a first crash in 66 seconds, AFLGo (directed fuzzing) in 336 seconds, and SymQEMU (concolic execution) produces 605 crashes after about 25 minutes. Each approach requires a dedicated harness and a set of seeds. And all of this applies to a single CVE. Empirical studies by the RAND Corporation estimate that developing a complete exploit takes 6 to 37 days. Compare that to the few hours a PSIRT team has per alert. Fuzzing remains essential for research, but it cannot serve as the mechanism for daily triage. The asymmetry is structural. A binary approach validated on a large scale The value of the presentation lay in the method it highlighted for overcoming this obstacle. Rather than relying on metadata, MOABI analyzes binaries, firmware, and containers as they are deployed. This allows for the generation of SBOMs directly from the executed code, including for statically linked components invisible to package managers (OpenSSL, zlib, libjpeg). It also enables the enrichment and rescoring of CVEs with KEV, EPSS, and SVCC data. Furthermore, it allows for the assessment of the actual hardening of binaries (ASLR, RELRO, NX, FORTIFY, stack canaries), a factor that CVSS cannot express but which radically changes a vulnerability’s priority. And to produce CBOMs (Cryptographic Bills of Materials) to prepare for post-quantum migrations on systems with lifespans of 10 to 20 years. For high-priority CVEs, the platform integrates with the Witchcraft Compiler Collection (WCC), an open-source framework that Jonathan has been developing for several years. The principle: transform an ELF executable binary into a library loadable via dlopen(), then directly call any function with arbitrary arguments via an embedded Lua interpreter. It takes just three commands to confirm a CVE on a stripped binary, in less than a millisecond, without source code. The tool has been validated on 3,861 production binaries spanning 14 processor architectures, and is now distributed in Debian, Ubuntu, and Kali Linux. Part of this work is the subject of a doctoral thesis defended at CNAM in 2026 and has already been presented at DEF CON 24, Black Hat Europe 2016, and USENIX WOOT 2024. Manufacturers who can relate to the problem The discussion that followed the presentation confirmed what many observers had suspected: regulatory pressure is no longer a theoretical governance issue. It has become a daily operational constraint for product safety teams, and audit automation is no longer an option. A particularly fruitful discussion took place with the SNCF teams, whose technical expertise and in-depth knowledge of the constraints of rail transport left a lasting impression on the session. The transportation sector clearly illustrates the current challenge: very long product lifecycles, a multitude of suppliers, critical embedded components, and now NIS2 obligations to meet across heterogeneous fleets accumulated over decades. One message kept coming up in the discussions: it is not so much the detection of vulnerabilities that poses a problem, but the ability to quickly distinguish what is truly urgent from what is merely noise. In an environment where volume will only increase, triage and prioritization are becoming the primary value-added functions of the modern PSIRT. Anything that can be automated upstream should be, to free up teams’ time for decisions that truly matter. A connection with other presentations at the conference One of the highlights noted by Jonathan was the presentation by Isabelle Olivier (Thales) on black-box analysis of security components. Her demonstration of

Read More »

40,000 CVEs a Year, 72 Hours to Respond: MOABI at Cyber On Board 2026

The third edition of Cyber On Board opens today on the Giens Peninsula: three days of scientific conferences, panel discussions, and exchanges centered on embedded cybersecurity, the resilience of critical systems, and technological sovereignty. The opening day sets the tone. Following the official welcome by Patrick Radja, VP Cybersecurity Director at Naval Group, the program moves into a keynote on AI and cybersecurity in embedded environments, followed by two substantial panels: one on technological sovereignty in the face of the rise of embedded AI, featuring representatives from NVIDIA, Valeo, and the French Gendarmerie; the other on regulation and cooperation at the heart of critical systems (rail, naval, aerospace), with SNCF, Alstom, and the French Navy’s General Staff. When Security Tools Become the Attack Vector The timing of this edition is especially telling. This past March, the cybersecurity community experienced a shock that captures, on its own, the very issues being addressed at Cyber On Board. On March 19, 2026, Trivy, one of the most widely used open-source vulnerability scanners in the world, developed by Aqua Security, was compromised in a sophisticated software supply chain attack. In other words, a tool designed to protect the software supply chain became the vehicle for its compromise. The mechanism is striking. Attackers force-pushed malicious code to 75 of the 76 version tags of Trivy’s official GitHub Action, turning the security scanner into a credential-stealing tool. In practice, the malicious code ran silently before the legitimate scanner, so workflows appeared to complete normally. Yet this tool runs at the heart of thousands of CI/CD pipelines, on every pull request, every merge, every deployment, with access to pipeline secrets by design. The outcome: cloud credentials, SSH keys, and Kubernetes tokens exfiltrated within hours. This episode reflects a deeper trend that the industry leaders gathered at Giens know well: attackers are moving upstream, increasingly targeting trusted tools, dependencies, and infrastructure rather than end applications. In this environment, relying solely on vendor metadata or version matching is no longer enough. It has become essential to analyze what actually runs in production. Tomorrow: Jonathan Brossard’s Presentation This is precisely the challenge that Jonathan Brossard, Founder and CTO of MOABI, will address in his talk on Wednesday, May 27, at 11:30 a.m., in the Software & Drone scientific conference session. His topic: practical vulnerability management under regulatory constraints for modern PSIRTs. This has become a structural challenge for product security teams. With more than 40,000 CVEs published in a single year, that is over a hundred new vulnerabilities every business day, and regulations such as the Cyber Resilience Act, NIS2, and DORA imposing remediation deadlines of 24 to 72 hours, traditional methods are reaching their limits. This is all the more true in embedded and industrial environments, where source code is sometimes no longer available, where firmware has been modified, and where life cycles span several decades. The Rest of the Week: Sessions Worth Watching Wednesday, dedicated to scientific conferences, brings together several major defense players. ArianeGroup will present its work on software obfuscation in industrial contexts and its integration into the development life cycle. Thales will speak on black-box analysis of security components, a subject closely related to MOABI’s own. Airbus Defence & Space will share lessons learned from the SOC dedicated to Airbus Helicopters products, while Naval Group will address the security evaluation of real-time embedded systems. Thursday continues this momentum with a strong focus on compliance and defense. Black Duck Software will open the day with the concrete impacts of the Cyber Resilience Act on R&D organizations, echoing directly the regulatory constraints raised by Jonathan. At 10:00 a.m., the MBDA x Alcyconie case study, presented by Stéphanie Ledoux, will focus on preparing embedded systems engineering teams for cyber crisis management, beyond the CERT perimeter alone. The French Navy will outline its approach to cyber training in the face of an exponentially growing threat, and KNDS will offer lessons learned from adopting post-quantum cryptography in vehicle computers and weapon systems. It is a program that confirms a fundamental shift: embedded cybersecurity is no longer a purely technical matter. It has become a regulatory, industrial, and strategic constraint for the entire sector. A full article covering Jonathan’s presentation and the discussions from these three days will follow later this week.

Read More »